![2023-Roseman_Labs-logomerk_color.png]](https://support.rosemanlabs.com/hs-fs/hubfs/2023-Roseman_Labs-logomerk_color.png?width=40&height=40&name=2023-Roseman_Labs-logomerk_color.png)
Design environment
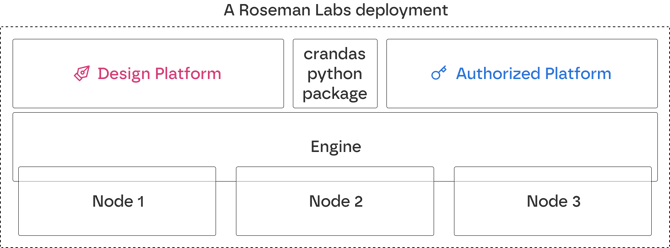
An analyst has the responsibility to design the script that will be executed. This can be done in crandas, by means of a design environment. Crandas can run in any analytics platform in which python packages can be installed and python scripts can be executed, such as (such as Jupyter notebook, spyder or Databricks). It generally runs locally on the analyst's own device. This Python analytics platform is connected to the design environment: a pair of platform and engine in which script signing is disabled.
In the design environment, the script can be thoroughly tested using dummy data before it is applied on production data. This environment is also used to record the script that is eventually imported to the authorized platform to be approved.
When recording a script, the analyst uses the "script.record()" functionality of crandas to transcribe the steps of which the analysis consists. These are then automatically stored into a .script file, which will be imported to the authorized platform.
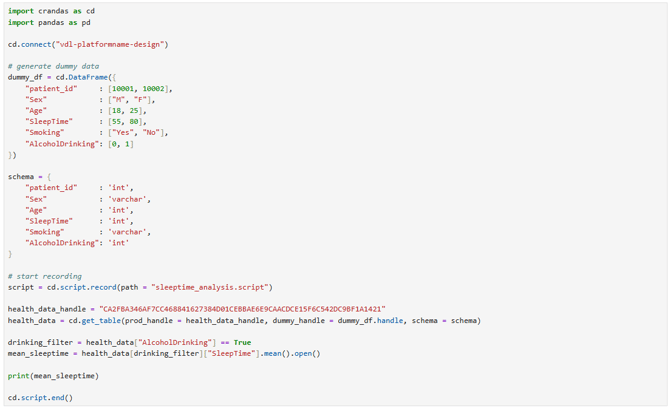
Script recording in design environment.
To test a script, the analyst needs data that is syntactically similar (same column names/same data types) to the actual source data that is processed in production. This is called "dummy data". This dummy data could be in the form of a csv or a DataFrame that you create.
Note that data that is processed in the design environment is not properly secured. Therefore, one should only work with dummy data here and never use sensitive data in the design environment.
Authorized environment
The authorized environment can be used to actually execute scripts that were created in the design environment and have been approved. Similar to the design environment, the authorized environment is connected to a local set up of crandas. However, in contrast to the design environment, the authorized environment has script signing/authorized mode enabled. The authorized environment is where the data providers import their sensitive data via the platform.
In the authorized environment, a script can only be executed when it has been signed by all approvers in the platform using their private keys. After approval, the script can then be executed on real data (must be executed in exactly the same order as the script was recorded).
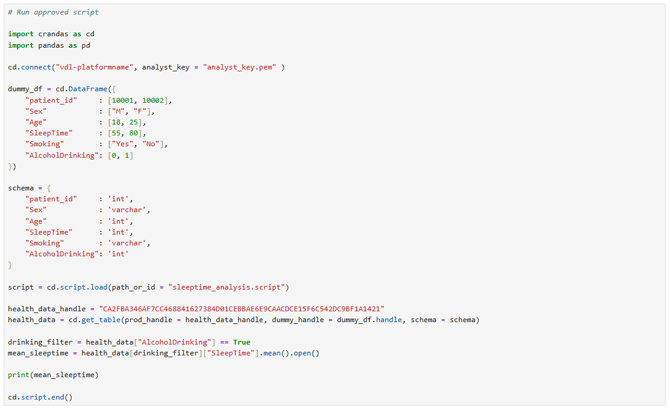
Running an approved script on production data by using 'cd.script.load'. The health_data_handle refers to data on the authorized platform, which is analyzed in this script.
For more information on using crandas, please refer to our documentation.